AI Security Blog
Session recaps and replays, guest posts, and notes from the people defending AI.
What Makes an AI Security Program Succeed?
Choosing the right third-party AI security vendor requires more than feature depth. Learn why and how intelligent platform architecture makes or breaks AI Security programs.
 OCTOBER 29, 2026
Recap: The EU CRA Is Coming
Nariman Aga-Tagiyev on the EU Cyber Resilience Act: who it covers, what's already live, what changes in December 2027, and where to start.
 OCTOBER 28, 2026
Recap: Getting Ahead of the Mythos Effect
Megan Horner of Seemplicity on what to do when AI finds vulnerabilities faster than your team can fix them: CTEM, validation and organizing work by the fix.
 OCTOBER 28, 2026
Rethinking Security From First Principles
AI has fundamentally changed software. Learn what security vendors and enterprises must rethink to secure AI adoption and realize ROI.
 OCTOBER 22, 2026
The Most Secure AI Feature Is Sometimes No AI
Before testing the prompt, ask whether the feature needs AI at all. An AppSec and AI pentesting view on attack surface, agency and a six-question decision framework.
 OCTOBER 19, 2026
Securing Agentic AI Skills
A SKILL.md file can shape what an agent reads, runs and sends. A practical review guide mapped to the OWASP Agentic Skills Top 10.
 OCTOBER 16, 2026
I Built an MCP Scanner. Here's What It Missed
A plain-English tour of MCP's trust risks, then a homemade scanner run against the paper's demo servers. Honest about what it missed.
 OCTOBER 15, 2026
Recap: How to Recover From an AI Breach
Geoff Burke of Object First on why Hugging Face had to rebuild from clean backups, what backing up AI covers, and how to know your restores will work.
 OCTOBER 6, 2026
The Revocation Gap
Revocation in MCP isn't one event. It's a race between your identity provider, your server's cache and the model's context, and agents act in the gap.
 OCTOBER 3, 2026
Stopping MCP Rug Pulls
An MCP client that ties approval to a tool's name can be fooled when the server quietly changes the tool afterward. A tested fix: fingerprint the approved contract and gate the call.
 SEPTEMBER 25, 2026
Recap: MCP Security Conference
Three hours, 1,200 registrants, an expert panel, five live security showcases, and new research on 31,000 MCP servers. Here's what you missed, and where to watch every session.
 SEPTEMBER 18, 2026
Authority Drift
A four-stage model — Delegation, Deference, Dependency, Detachment — for how decision authority slips from accountable people to automated systems, drawn from failures from Knight Capital to Durban to the Boeing 737 MAX, and applied to AI agents and MCP in Africa.
 SEPTEMBER 17, 2026
We Built Minority Report. It’s Just Not What We Expected.
From predictive-policing algorithms and AI risk scores to facial recognition and tools like Cybercheck and COMPAS, AI is quietly reshaping policing, courts, and criminal justice — sometimes solving cold cases in days, sometimes jailing the wrong person.
 SEPTEMBER 11, 2026
The Over-Powered Tool Problem in MCP
Even an MCP tool nobody tricked is a liability if it holds more authority than the task needs. A hands-on GitHub lab on the over-powered tool problem — and least privilege.
 SEPTEMBER 8, 2026
Stale Privilege Detection for MCP
In MCP, permissions quietly outlive the policies that granted them. A practical framework for detecting stale privileges — collect, diff, score, reconcile — before an attacker exercises the gap.
 SEPTEMBER 4, 2026
The MCP Configuration Drift Problem
MCP's discovery protocol broadcasts a drifted setting to every connected tenant — turning one small config change into enterprise-wide exposure, and what to do about it.
 SEPTEMBER 3, 2026
Why OAuth Breaks Differently for AI Agents: The Long-Lived Token Problem
Autonomous agents outlive the sessions OAuth assumes. How long-lived agent tokens create replay, scope creep and revocation gaps, and what to do about it.
 SEPTEMBER 3, 2026
AI Recommends, Humans Decide: Responsible AI Inside a Bank
Abhijit Dey (Axis Bank) on what responsible AI actually means — cautious tokens, agents managed like employees, a separate AI gateway, and why AI should recommend, never decide, when the outcome affects a person.
 AUGUST 31, 2026
BOLA: The Seven-Year Cybersecurity Itch
BOLA has topped the OWASP API Security Top 10 since 2019. Darren Shelcusky on why seven years of detection hasn't fixed it — and why agentic AI turns a known engineering failure into an urgent one.
 AUGUST 23, 2026
Autonomous Authority Without Autonomous Safety
Enterprises are giving AI agents Level 5 authority with Level 3 controls. Darren Shelcusky on why 'a human in the loop' is really a human at the end of the loop — and why boundaries matter more than prompts.
 JULY 30, 2026
He Bought a Used Car. The App Let Him Take Over Anyone's.
Researcher Vishal Bhaskar took over any vehicle's account through a public VIN and a login code with no rate limit, and explains why agentic AI makes the next attack trivial.
 JULY 1, 2026
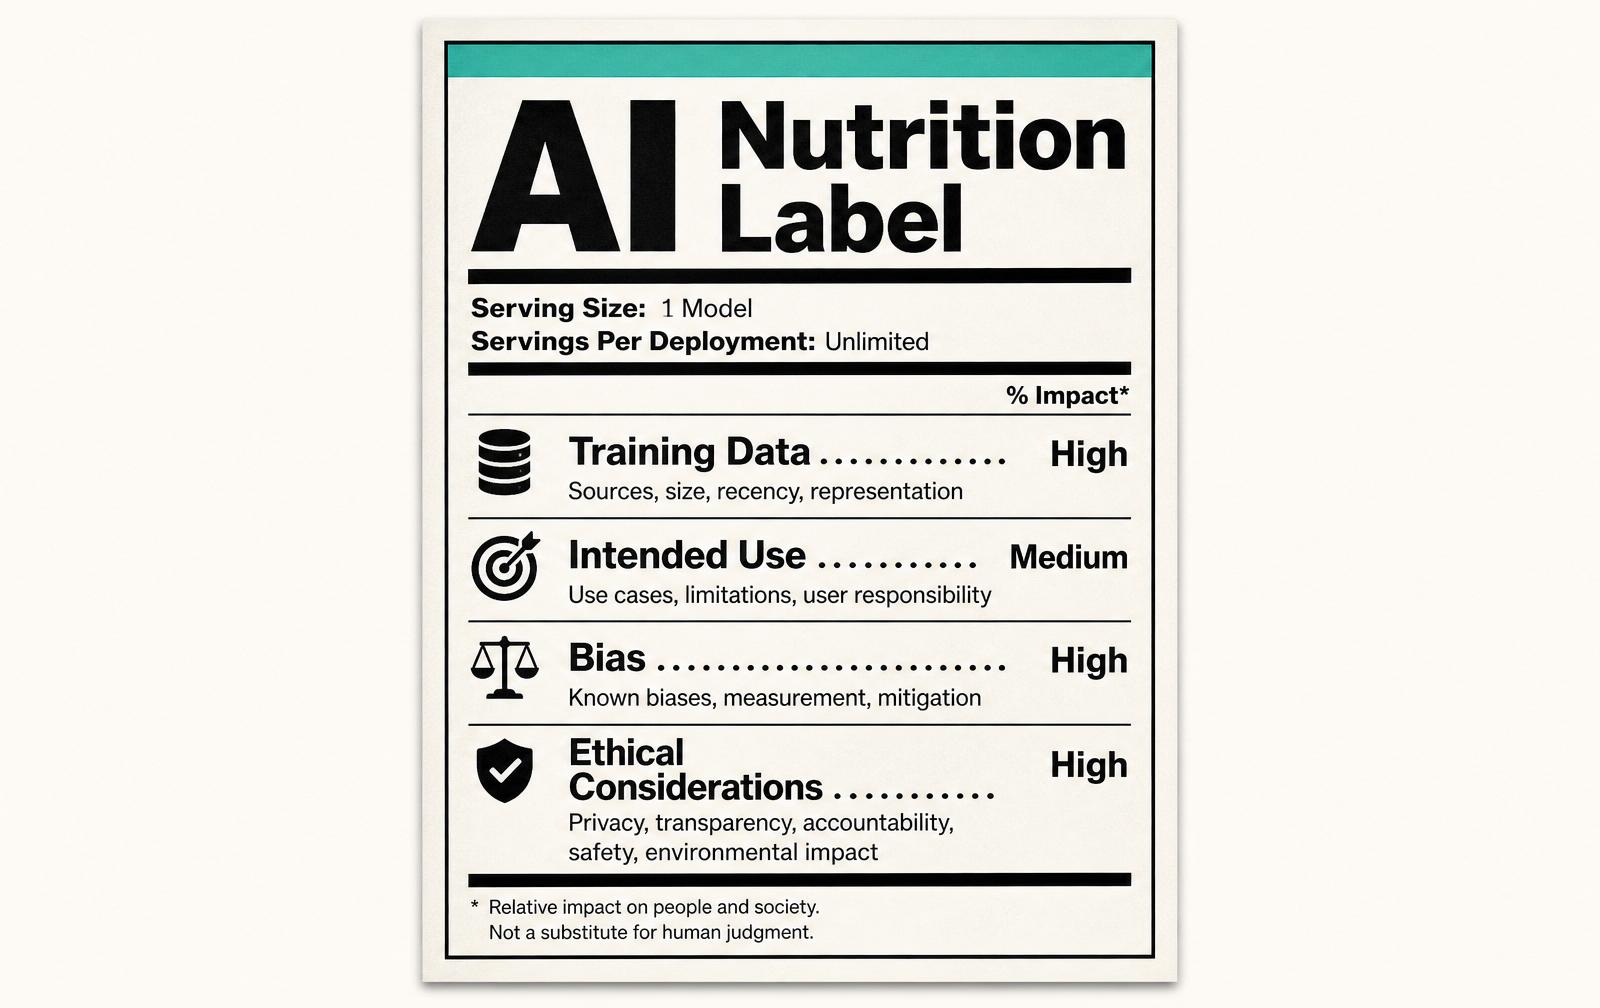
The AI Nutrition Label: Why Model Cards Matter
Model cards were meant to be the nutrition label for AI — a plain-language summary of what's inside a model. A decade in, they're voluntary, inconsistent, and often missing, just as regulators start demanding real transparency.
 JUNE 29, 2026
The Two Faces of AI in Automotive Security: A Conversation Among Practitioners
Florian Rohde moderates a panel with Jennifer Tisdale, Moe Yassine, and Kartheek Kumar on AI as both threat and defender's tool in automotive security.
 JUNE 29, 2026
Governing AI Security on Wheels: The GRC Maturity Gap in Automotive
Sai Anand on the 92% remote attack rate, the BIS rule, and why most automotive OEMs are stuck at Level 2–3 on AI/API governance even when they're at Level 4 on traditional cybersecurity.
 JUNE 29, 2026
Why Your Automotive ML-Based IDS Is an Asset, Not a Control
Tyson Benson (Clarios) on the TARA mistake coming for automotive cybersecurity — and how to treat ML-based intrusion detection systems before they ship.
 JUNE 29, 2026
A Gearhead's Guide to AI Hacking: Why Most "AI Security" Doesn't Work
Chuck Herrin breaks down AI's insecurable attack surface using analogies from his car collection. Why guardrails can't reach 100%, what NIST's June 2026 proof means, and what defenders should actually do.
 JUNE 23, 2026
Vibe Coded and Vulnerable: The Hidden Security Cost of Letting AI Write Your Code
AI coding assistants ship faster — and ship more vulnerabilities per line. A security engineer's field guide to vibe coding, slopsquatting, and treating model output as untrusted input.
 JUNE 22, 2026
The Math Behind Why AI Guardrails Will Always Fail Eventually
A NIST mathematician used a 95-year-old proof from Kurt Gödel to formally show that no fixed set of AI guardrails can ever be complete — and what that means for how we secure AI going forward.
 JUNE 12, 2026
Stop Slowing Down AI. Your Security Team Should Be Leading It.
Raj Umadas on why security teams should lead AI adoption — not gatekeep it. Builders first, default to yes, and the mechanics that actually close the find/fix gap.
 JUNE 4, 2026
Is Your LLM Lying to You? What Testing 21 Models Revealed
Scott Bly built Hermia, an open-source LLM eval framework, and ran 21 models across three inference backends. The results break a few assumptions security teams are still operating on.
 MAY 28, 2026
Kin Lane: A $125K AWS Bill, Overnight
Kin Lane woke up to a $125,000 AWS bill. The story isn't about the money — it's about how a single exposed credential turned into six figures of damage in under eight hours.
 MAY 21, 2026
AI Agents Don't Use Your App. They Hit the API.
A conversation with Darren Shelcusky on what changes when the caller isn't a person — and why a decade of security investment sits at the wrong layer.
 MAY 18, 2026
Two AI Attacks in One Week. The Defensive Playbook Just Broke.
Apple's MIE walked around in five days. The first AI-built zero-day shipped against a real target. The disclosure-and-patch cycle was calibrated to an attacker that doesn't exist anymore.
 MAY 12, 2026
MCP Just Got Its First Real Attacks. The Pattern Behind Them Is Worse.
Two pieces of MCP attack research landed this week. Both reproducible. Both pointing at the same design flaw in how agentic coding tools handle trust.
This Week in AI Security
The AI security stories that matter, every Sunday. Free on Substack.